Daily threat intel, interactive tools, and an expanding library of security education — all free, all sourced, no fluff.
Subscribe via RSS
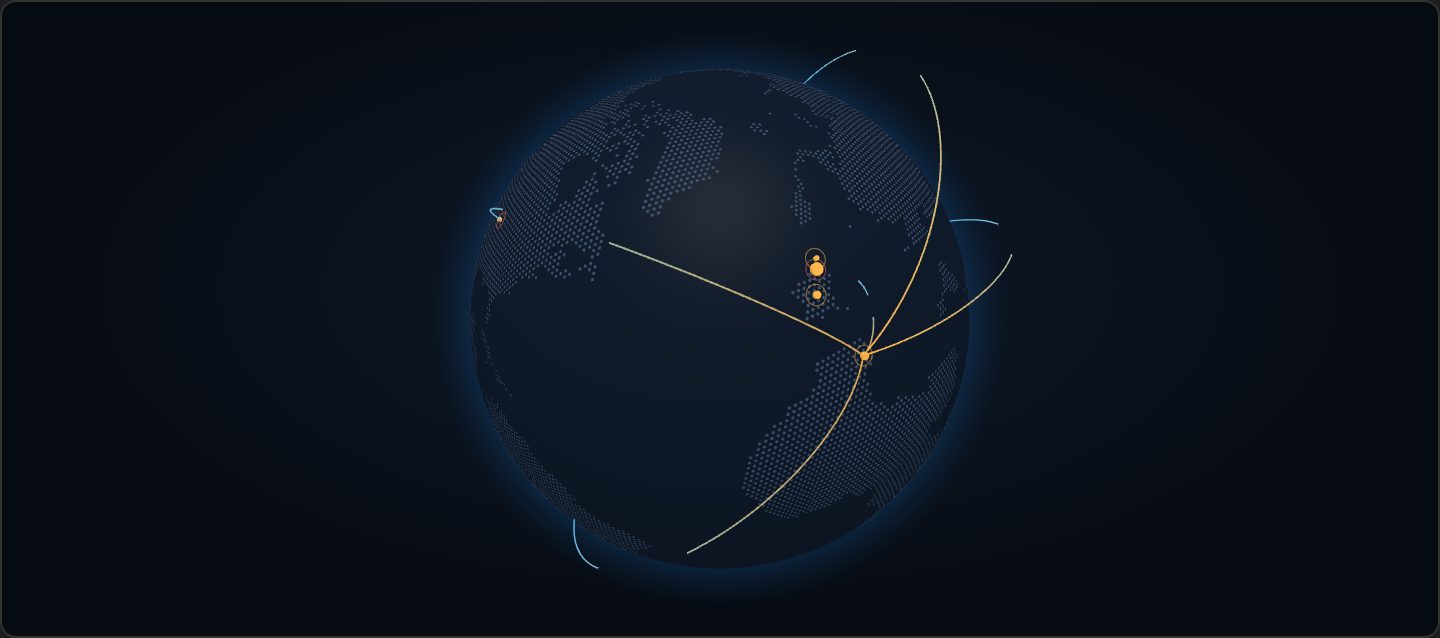
🌐 Global Threat Map
Who used this site's decoy AWS keys, by country
–
Key uses, last 24h
–
Hand-offs
–
Countries
🔬 Featured Research
In-depth threat intelligence and practitioner guides
Threat Intel
Kali365: The PhaaS Platform Weaponizing Microsoft Auth Against You
FBI-flagged PhaaS platform abusing device code flow to steal OAuth tokens and bypass MFA entirely.
Jun 16, 2026
Threat Intel
Device Code Phishing — The Attack That Makes MFA Irrelevant
How nation-state actors exploit OAuth 2.0 device auth flow to hijack M365 accounts without stealing credentials.
Jun 2, 2026
Orange Book
2026 Verizon DBIR: What the Data Actually Means for Defenders
Practitioner breakdown of the 2026 DBIR — vulnerability exploitation, ransomware, third-party risk, and GenAI in the attack chain.
Jun 5, 2026
📙 Latest from the Orange Book
Deep-dives, framework breakdowns, and technical explainers
Who actually uses a leaked AWS key? Tracing it with rotating canaries
I put fake AWS keys on my site and changed them every day. Most of the people who used them had …
Oct 8, 2026
What Is the Android Zero Touch Portal, Actually?
How the Zero Touch Portal links your organization to a device reseller, what a provisioning …
Aug 16, 2026
Part 4: Android App Management and Managed Google Play
How Managed Google Play connects to Intune, the difference between required vs. available …
Aug 16, 2026